CTF Challenge: Web Exploitation
Table of contents:
Introduction to challenge and description
Solution walkthrough
Conclusion
Event: BUG BOUNTY BLITZ
Challenge Name: Forbidden Path
Category: Web Exploitation
Points: 150
Introduction:
A web exploitation Capture The Flag (CTF) challenge is a cybersecurity competition exercise where participants must identify and exploit security vulnerabilities in a purposefully vulnerable web application to find a hidden piece of information, known as a "flag".
It tests practical skills in areas like reconnaissance, input testing, and exploiting common flaws such as SQL injection, XSS, or file inclusion, providing a safe way to learn real-world web security concepts.
Description of the challenge:
Some paths are meant to be invisible, written only for eyes that wander where the world does not. A quiet list sleeps in the shadows of the site — the guide to what should stay hidden waits at the very root, and you might uncover a line never meant to be seen.
Solution Walkthrough
Step 1: Reading the description
The challenge description hinted that something hidden within the site’s structure would lead to the flag — a clear sign that this was a web directory problem.
Key clue: “A quiet list sleeps in the shadows of the site” — “quiet list” is often the robots.txt file, which lists directories that search engines shouldn’t index.
Step 2: Checking robots.txt
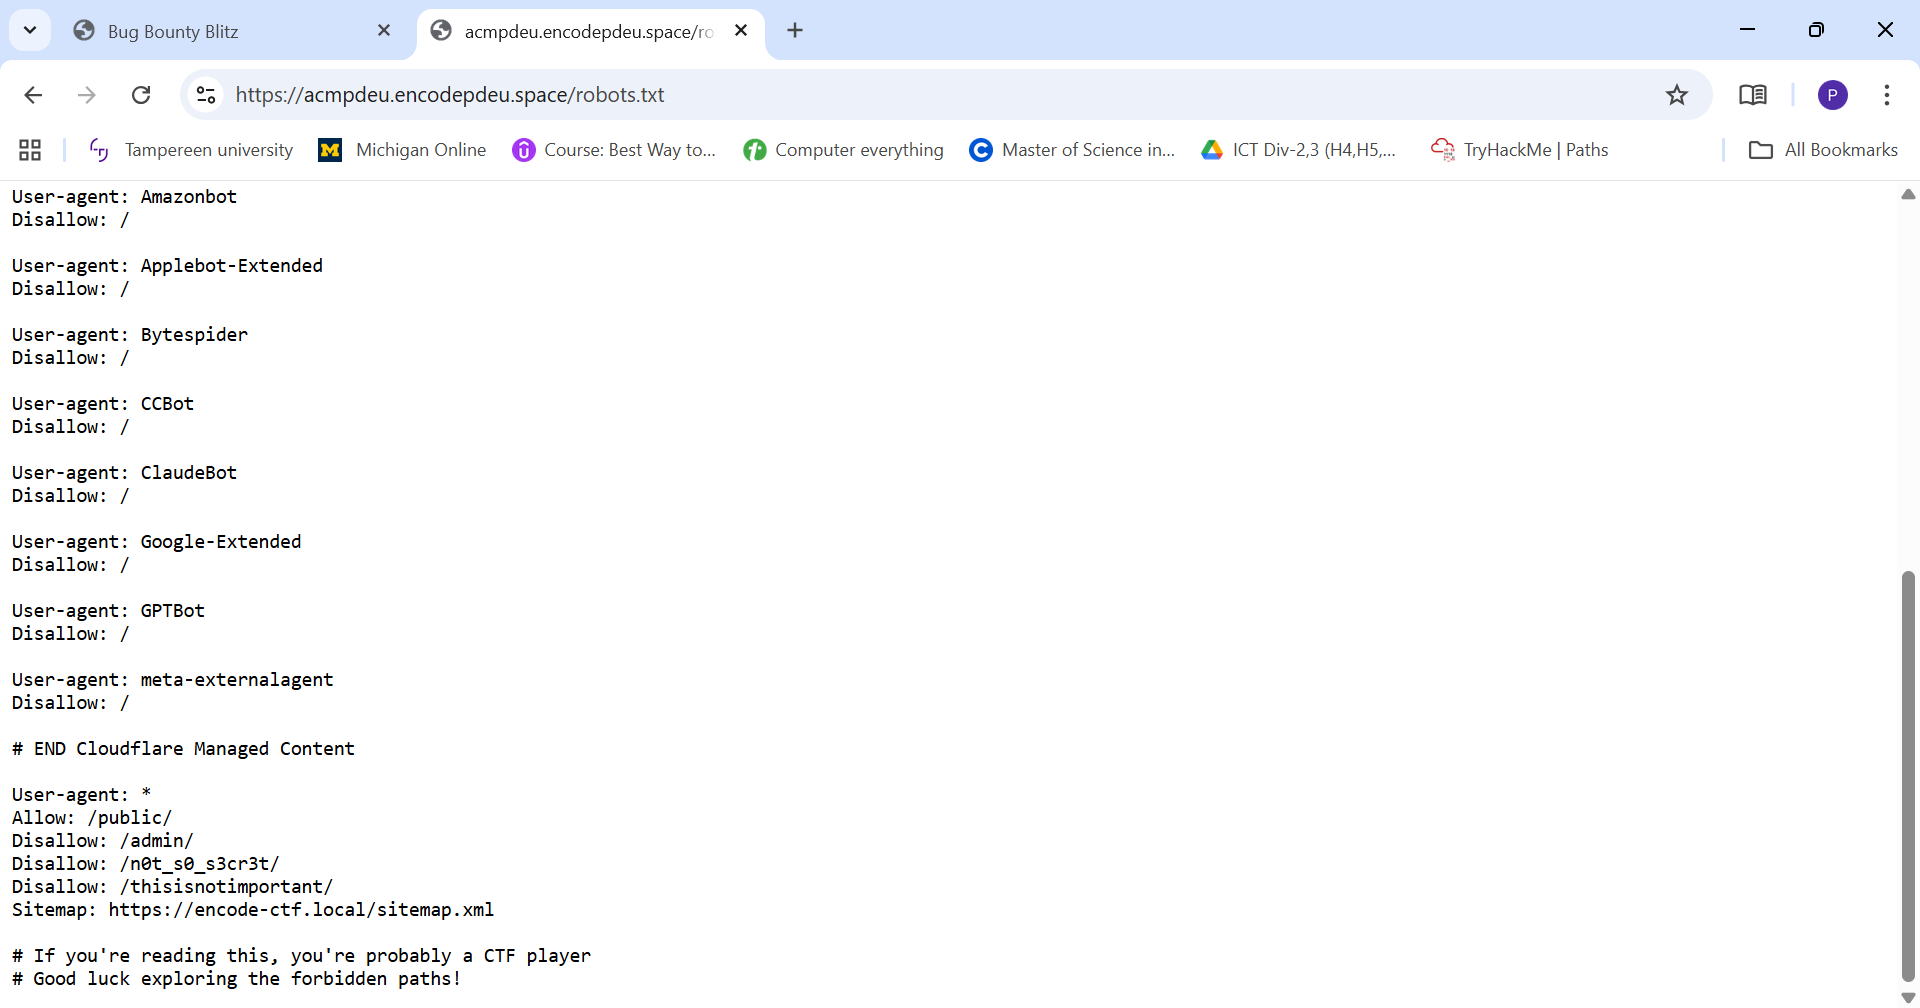
At the website root, after opening: https://acmpdeu.encodepdeu.space/robots.txt
This file showed several “Disallow” paths:
User-agent: *
Allow: /public/
Disallow: /admin/
Disallow: /n0t_s0_s3cr3t/
Disallow: /thisisnotimportant/
This revealed a suspicious directory:
/n0t_s0_s3cr3t/
Step 3: Exploring the hidden directory
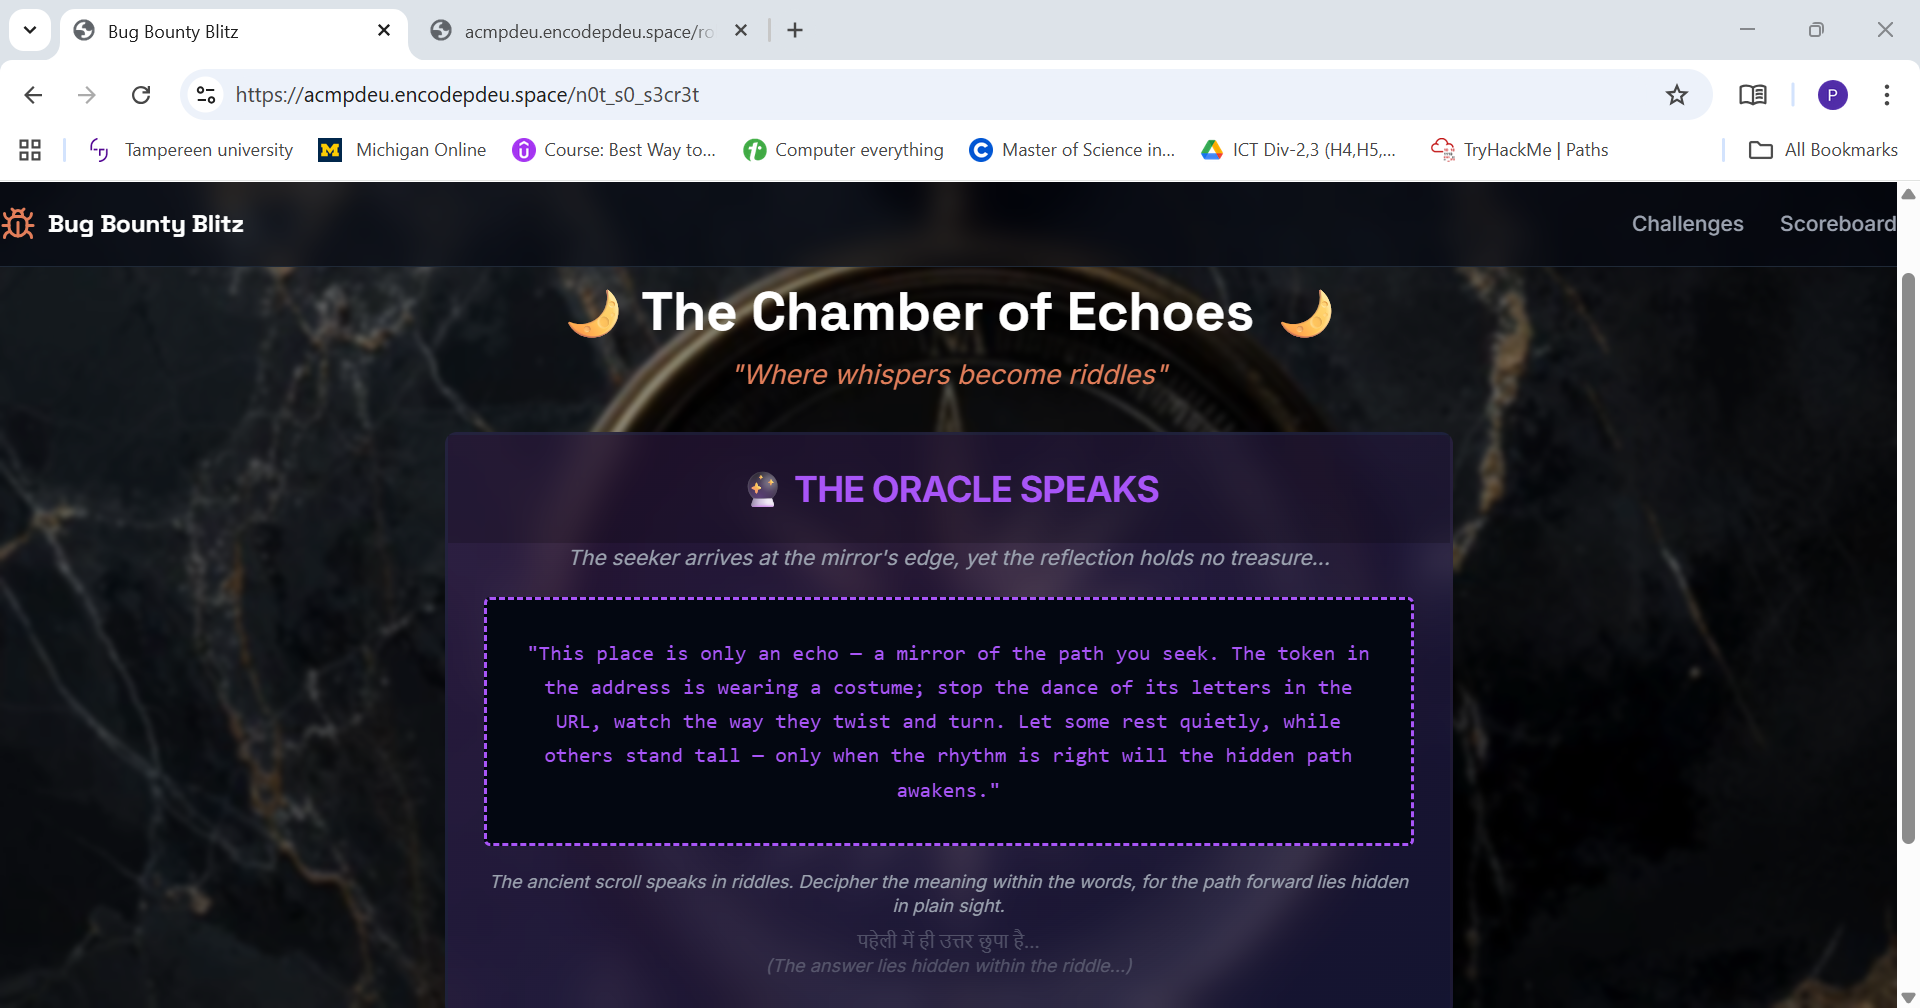
Visiting that directory revealed a riddle:
https://acmpdeu.encodepdeu.space/n0t_s0_s3cr3t/
Riddle:
"This place is only an echo — a mirror of the path you seek. The token in the address is wearing a costume; stop the dance of its letters in the URL, watch the way they twist and turn. Let some rest quietly, while others stand tall — only when the rhythm is right will the hidden path awakens."
The riddle clearly referenced the directory name itself — saying it’s “wearing a costume”, meaning it’s encoded.
Step 4: Decoding the disguised token
The directory name n0t_s0_s3cr3t looked a bit different so by replacing the numbers with similar-looking letters we’ll check if it’s a possible solution.
0 → o
3 → e
So:
‘n0t_s0_s3cr3t’ changes to → ‘not_so_secret’
The phrase “stop the dance of its letters” hinted at removing unnecessary characters so I removed the underscores and the resulting text was:
‘notsosecret’
Step 5: Accessing the real hidden path
Replacing the text in the url:
https://acmpdeu.encodepdeu.space/not_so_secret
The flag was successfully found!
Step 6: Flag
FLAG{ NOT_SO_SECRET}
Conclusion
The Forbidden Path challenge demonstrated how seemingly hidden or restricted areas of a website can still be discovered through careful observation and logical reasoning. By analyzing the challenge description, inspecting the robots.txt file, and decoding leet-speak patterns, I successfully uncovered the hidden directory and obtained the flag.
This challenge emphasized the importance of exploring beyond visible web pages and understanding how web crawlers and access restrictions work.